11 September 2026
Reporting obligations
Actively exploited vulnerabilities and severe incidents must be reported within 24 hours, for every product already on the EU market (Art. 14).
Templates, plain-language guides and a fully worked example that take a manufacturer from "Does the CRA apply to us?" to a signed EU declaration of conformity.

The CRA applies in stages. Reporting is already mandatory, full conformity follows in December 2027, and the duties then run for as long as you support the product.
Actively exploited vulnerabilities and severe incidents must be reported within 24 hours, for every product already on the EU market (Art. 14).
Products placed on the EU market must meet Annex I, pass conformity assessment and carry the CE marking.
Handle vulnerabilities and ship security updates, in most cases for at least five years (Art. 13(8)), and keep the technical file for at least ten years (Art. 13(13)).
The kit is files, not a platform. You work in Word and Excel on your own systems, and nothing about your products leaves your company.
No account, and no upload of source code, SBOMs, unpatched vulnerabilities or incident details. The most sensitive information a manufacturer holds stays on its own systems.
There is no cloud service for your security team or procurement to assess first. Download today, start tomorrow.
The CRA asks you to keep the technical documentation for at least ten years (Art. 13(13)). Word, Excel and PDF files remain readable long after any subscription has ended.
One price. No subscription and no fees per product or per user. Updates until at least the end of 2027 are included.
What the kit does not do: it does not scan your code or monitor vulnerabilities. Keep the tools you already use for that; the kit shows which evidence the CRA expects from them.
Compare the options:Consultant, platform or template kit: which one still works for you in five years?
Every template has a completed counterpart for the Lumora TH-200, a fictional smart thermostat: risk register, evidence matrix, technical file, EU declaration and reporting exercise. Start with the free 4-page overview.
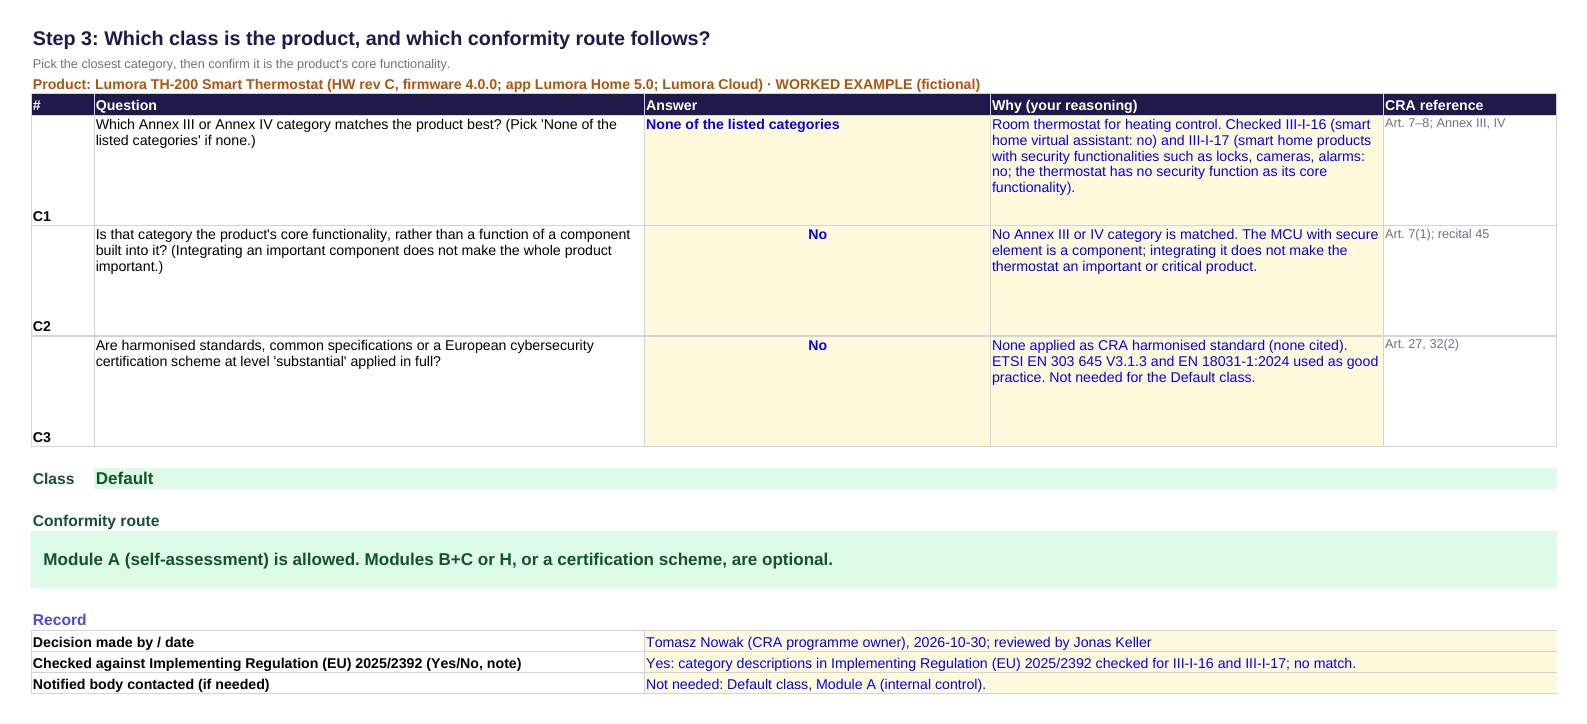
Scope decision: in scope, manufacturer, default class, Module A
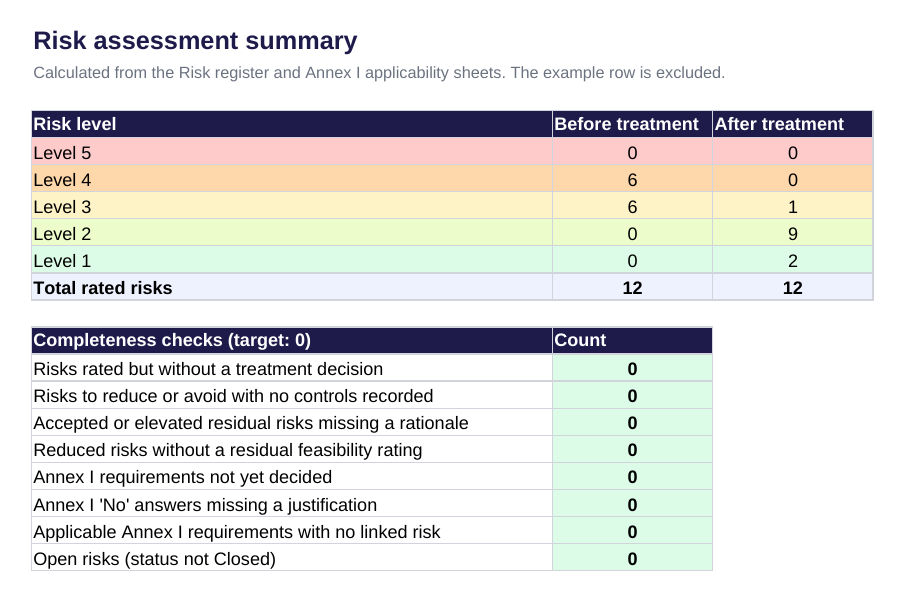
Risk assessment: 12 risks, from firmware tampering to loss of heating in winter; every completeness check at zero
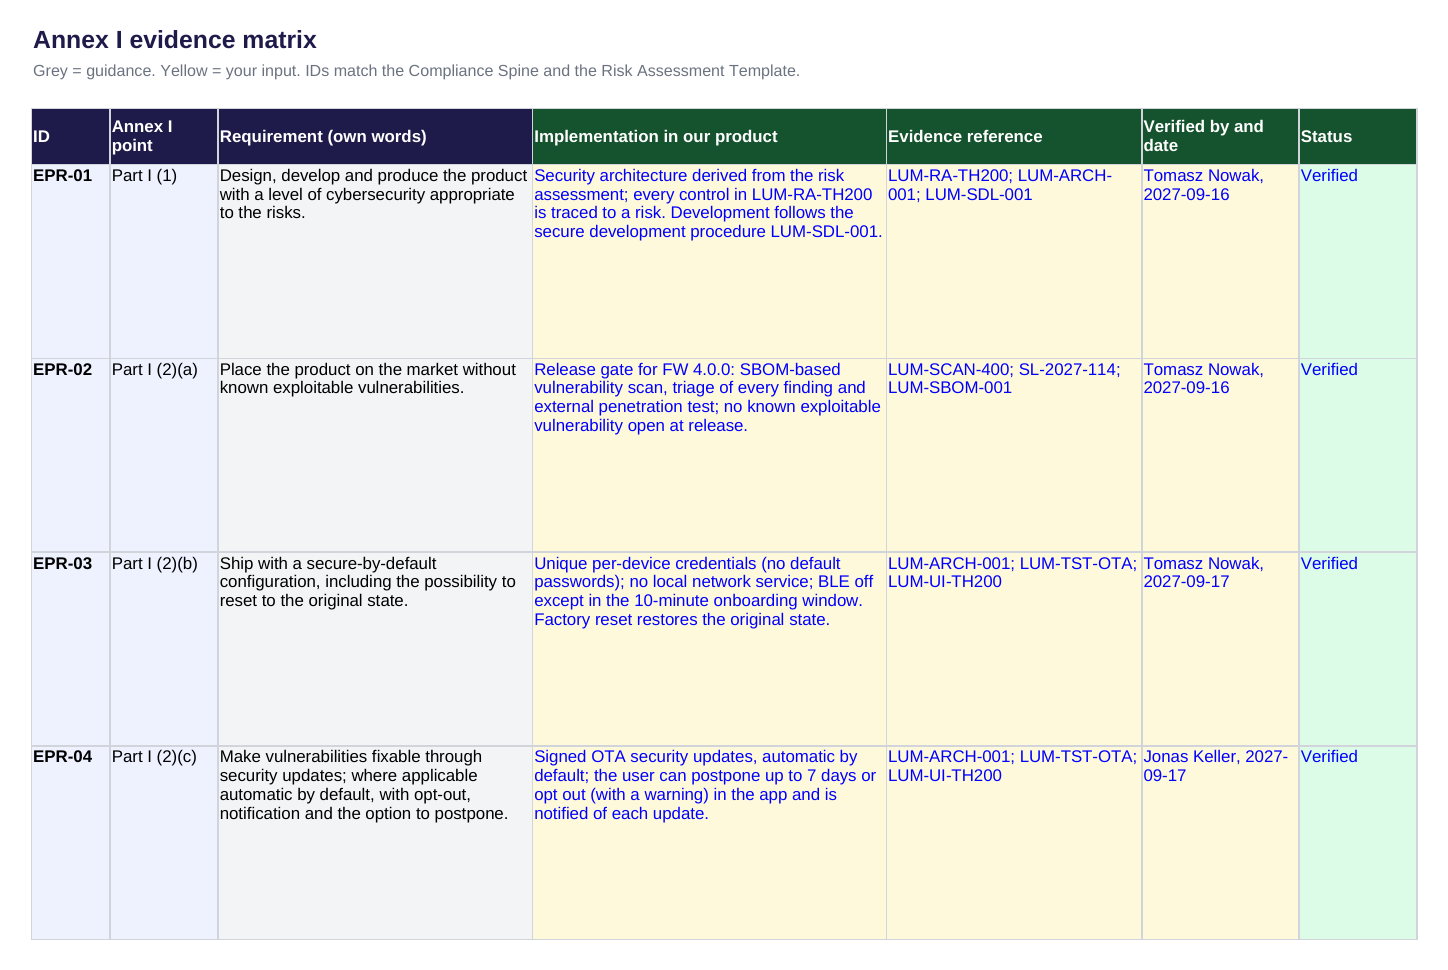
Annex I evidence matrix: 22 requirements, each with its proof
The 24 filled example files come with the full kit.
Lumora Home Technologies GmbH and Lumora TH-200 are fictional.
Özer Koray Akdemir is a product cybersecurity architect. He built a product cybersecurity function under a regulation that was still new and took it through audit and type approval. The kit turns that experience into documents a small team can complete.
About the author →